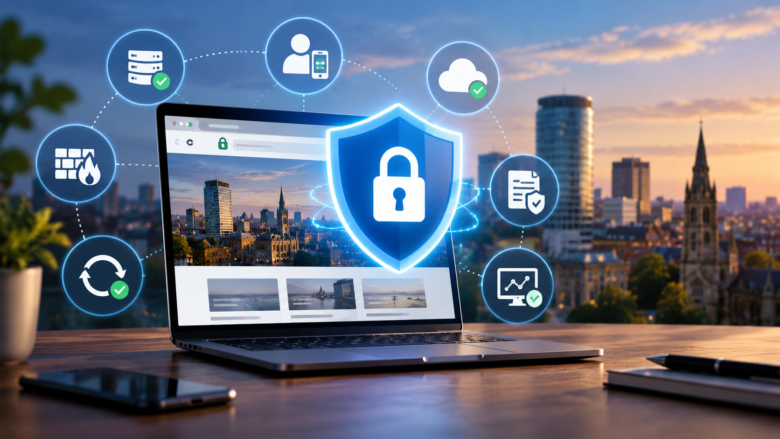
Keeping your Birmingham website secure does not have to feel overwhelming. Most attacks do not involve highly skilled hackers breaking through complicated systems—they happen because of outdated software, weak passwords, missing backups, or unmonitored admin accounts. The good news is that these are all fixable with a clear plan.
Whether you run a local service business, an online shop, a restaurant, a law firm, or a growing company in Birmingham, your website is often the first place customers meet your brand. It may collect enquiries, bookings, payments, newsletter sign-ups, or personal details. That makes website security a business priority, not just a technical task.
This guide explains how to enhance your website security step by step, using practical measures that suit small and medium-sized Birmingham businesses.
Why Website Security Matters for Birmingham Businesses
Your website is more than an online brochure. It is a digital storefront, a lead-generation tool, a booking system, and sometimes a payment platform. If it goes down or gets hacked, the impact can reach far beyond your website.
A security problem can lead to:
- Lost sales and enquiries
- A damaged reputation
- Customer data being exposed
- Google warnings or removal from search results
- Downtime while your site is repaired
- Costly emergency fixes
- Potential data protection issues under UK GDPR
Cybercriminals often use automated tools to scan thousands of websites at once. They look for easy targets: outdated plugins, weak admin passwords, unsecured forms, and sites without two-factor authentication. This means even a smaller Birmingham business can be targeted simply because its website has a common weakness.
Security is also closely linked to trust. Visitors are more likely to complete a contact form, make a booking, or buy from you when your website looks professional and secure. An SSL certificate, clear privacy information, and a site that loads properly all help reassure people that their details are safe.
Start With the Essentials: HTTPS and SSL
One of the first things to check is whether your website uses HTTPS rather than HTTP. HTTPS encrypts the connection between your visitor’s browser and your website server. This helps protect information such as names, email addresses, passwords, and payment details while it travels across the internet.
If your website still shows “Not secure” in the browser, fix this as soon as possible. An SSL certificate is usually included with reputable hosting packages, and free options such as Let’s Encrypt are widely available.
To strengthen this area:
- Install an SSL certificate on your domain
- Force all traffic from HTTP to HTTPS
- Check that images, scripts, and forms also load securely
- Set reminders to monitor certificate renewals
- Test your SSL setup using a tool such as SSL Labs
HTTPS alone will not make your website invincible, but it is an essential first layer. It protects data in transit and helps prevent browsers from warning visitors that your site may be unsafe.
Use Strong Logins and Two-Factor Authentication
Weak or reused passwords remain one of the easiest ways for attackers to access a website. If someone gains access to your admin area, they may be able to change pages, install malicious code, steal customer data, or take your site offline.
Start by reviewing every account connected to your website, including:
- Your CMS login, such as WordPress
- Hosting control panel
- Domain registrar account
- DNS settings
- Email accounts
- Third-party plugins or tools
- Developer and agency accounts
Use a unique, long password for each account. A password manager can create and store strong passwords so you do not have to remember them all.
Then enable two-factor authentication, also known as 2FA or MFA. This adds a second step after entering your password, usually a code from an authenticator app. Even if someone obtains your password, they cannot log in without that second verification step.
For the best protection, enable 2FA on:
- Website admin accounts
- Hosting accounts
- Domain and DNS accounts
- Email accounts
- Cloud storage accounts
- Any account with access to customer data
It is also wise to remove old accounts. If a former employee, freelancer, or agency no longer needs access, delete or downgrade their login immediately. Give each person only the access they genuinely need.
Keep Your Website Software Updated
Outdated software is one of the most common reasons websites get compromised. This includes your CMS core, themes, plugins, extensions, server software, and any third-party integrations.
If you use WordPress, for example, updates may be available for WordPress itself, your theme, and individual plugins. Each outdated component can create a potential entry point for attackers.
Create a simple update routine:
- Check for updates at least weekly
- Apply security updates as soon as possible
- Back up your website before major updates
- Remove plugins and themes you no longer use
- Avoid installing plugins from unknown sources
- Check that your plugins are actively maintained
Inactive plugins can still create risk. If you are not using a plugin, it is usually safer to delete it rather than leave it disabled on your site.
Before updating, take a backup. If an update causes a conflict or breaks part of your website, you can restore a recent version quickly. This is especially important for e-commerce sites, booking systems, and websites with custom functionality.
Protect Your Website With a Firewall
A firewall acts like a security guard for your website. It monitors incoming traffic and blocks suspicious requests before they reach your site. A web application firewall, or WAF, can help protect against common attacks such as malicious bots, brute-force login attempts, SQL injection, and cross-site scripting.
Many hosting providers offer firewall protection, while security tools such as Cloudflare can add another layer of defence. A WAF is particularly useful if your website receives a lot of traffic, handles payments, or has public forms.
A firewall can help with:
- Blocking suspicious IP addresses
- Reducing bot traffic
- Preventing repeated login attempts
- Filtering malicious requests
- Reducing the risk of certain common attacks
- Supporting protection during traffic spikes or DDoS attempts
Firewalls work best alongside other security measures. They cannot replace strong passwords, updated software, or reliable backups, but they can stop many obvious attacks before they cause damage.
Back Up Your Website Properly
Backups are your safety net. If your website is hacked, corrupted, accidentally deleted, or affected by a faulty update, a clean backup can help you restore it quickly.
A good backup plan should include:
- Automatic daily backups
- Off-site storage, not only on your hosting server
- Separate backups for website files and databases
- Multiple restore points
- Regular testing to confirm backups actually work
- Secure access to backup accounts
The 3-2-1 approach is a useful rule: keep three copies of important data, store them on two different types of storage, and keep one copy off-site or offline. For a website, this could mean a live version on your host, a cloud backup, and another secure backup stored elsewhere.
The most important part is testing. A backup you have never restored is not much use during an emergency. Schedule a test restore every few months, ideally on a staging site, and confirm that your pages, images, forms, and database all work correctly.
Secure Your Forms and Customer Data
Contact forms, booking forms, newsletter sign-ups, and checkout pages are common targets because they collect information from visitors. Even a simple enquiry form may collect names, email addresses, phone numbers, and messages.
To improve form security:
- Use spam protection such as reCAPTCHA or honeypot fields
- Limit submission attempts
- Validate information on the server, not only in the browser
- Avoid collecting data you do not need
- Encrypt data in transit with HTTPS
- Store only necessary customer information
- Restrict access to form submissions and databases
- Use reputable form plugins and keep them updated
If your website handles payments, use a trusted payment provider such as Stripe, PayPal, or another established gateway. Avoid storing full card details on your own server unless you have the correct security controls and compliance processes in place.
You should also review your privacy policy and cookie settings. Be clear about what data you collect, why you collect it, how long you keep it, and who can access it. This supports customer trust as well as UK GDPR compliance.
Choose Secure Hosting and Manage Access Carefully
Your hosting provider plays a major role in website security. A reliable host should offer more than just space for your website files. Look for features such as SSL support, firewalls, malware scanning, automatic backups, uptime monitoring, and responsive technical support.
When choosing or reviewing hosting, ask whether the provider includes:
- Daily automated backups
- Server-level firewall protection
- Malware scanning
- SSL certificate management
- Staging environments
- Support for the latest PHP or server versions
- Clear recovery procedures
- Two-factor authentication for account access
It is also important to control who can access your hosting and admin areas. Avoid shared logins. Instead, create separate accounts for each team member, contractor, or agency. Give administrators access only to people who truly need it, and use lower-level roles for content editors.
If your developer built the site, ask them to confirm that you have ownership of your domain, hosting, CMS, and all relevant accounts. This makes it easier to manage security and avoid problems if your working relationship changes.
Monitor Your Website for Warning Signs
Website security is not something you set once and forget. Regular monitoring helps you spot problems early, before they become serious.
Set up alerts or checks for:
- Failed login attempts
- New admin users
- Unexpected file changes
- Plugin or theme updates
- Sudden drops in traffic
- Unusual spikes in traffic
- Website downtime
- SSL certificate expiry
- Google Search Console security warnings
- Suspicious redirects or pop-ups
Google Search Console is particularly useful because it can alert you if Google detects malware, phishing, or other security issues on your site. If your website suddenly starts redirecting visitors to strange pages, showing unfamiliar ads, or loading much more slowly than usual, investigate immediately.
You can also use uptime monitoring tools to notify you if your website goes offline. Fast detection can reduce downtime and limit the damage caused by an attack.
Train Your Team to Spot Phishing
Even the best technical security can be undone if someone clicks a fake link or shares login details with the wrong person. Phishing emails often pretend to come from your hosting provider, domain registrar, bank, CMS platform, or even a colleague.
Modern phishing messages can look very convincing. They may use your business name, mimic a supplier’s branding, or create a sense of urgency by claiming that your account will be suspended.
Train everyone who manages your website to:
- Never share passwords by email or message
- Check the sender’s email address carefully
- Avoid clicking links in unexpected emails
- Go directly to a website by typing the address rather than using an email link
- Verify requests for password resets or payment changes by phone
- Report suspicious messages immediately
- Use a password manager rather than saving passwords in browsers or documents
A simple rule helps: if an email asks for login details, payment changes, or urgent action, verify it through a separate trusted channel before acting.
Create a Simple Incident Response Plan
No security setup is perfect. What matters is how quickly and calmly you respond if something goes wrong. A one-page incident response plan can save valuable time.
Your plan should include:
- Who is responsible for website security
- Contact details for your hosting provider, developer, and IT support
- How to access backups
- Which accounts need password changes first
- How to take the website offline if needed
- How to restore from a clean backup
- Who will assess whether customer data was affected
- When to contact the ICO if personal data may have been exposed
- How to communicate with customers if necessary
If a breach involves personal data and is likely to create a risk to individuals, UK GDPR generally requires assessment and, where necessary, reporting to the Information Commissioner’s Office within 72 hours of becoming aware of the incident. Even if you are unsure whether reporting is required, keep a written record of what happened and the steps you took.
Consider Cyber Essentials Certification
Cyber Essentials is a UK government-backed scheme that helps businesses put basic cyber security controls in place. It focuses on practical areas such as firewalls, secure configuration, access control, malware protection, and security updates.
For Birmingham businesses, Cyber Essentials can be useful for several reasons:
- It provides a clear security framework
- It shows customers and partners that you take security seriously
- It may support tender and contract requirements
- It encourages consistent security habits
- It can help identify gaps in your current setup
You do not need certification to have a secure website, but working towards its principles can help you build a strong foundation. If you handle sensitive customer data or work with larger organizations, it may be especially worthwhile.
A Practical Website Security Checklist
Use this checklist to review your Birmingham website today:
- Your website uses HTTPS with a valid SSL certificate
- All admin, hosting, email, and domain accounts use unique passwords
- Two-factor authentication is enabled wherever possible
- Old user accounts have been removed
- CMS, plugins, themes, and server software are updated
- Unused plugins and themes have been deleted
- Automatic backups run daily and are stored off-site
- Backups have been tested with a real restore
- A firewall or WAF is in place
- Forms use spam protection and secure data handling
- Access is limited to people who need it
- Security alerts and uptime monitoring are active
- Staff know how to spot phishing emails
- You have a simple incident response plan
- You review security settings at least monthly
Enhancing Website Security
Enhancing the security of your Birmingham website does not require a huge budget or an in-house technical team. It requires consistent attention to the basics: secure logins, updated software, reliable backups, monitored access, and a clear plan for emergencies.
Start with the highest-impact actions first. Enable two-factor authentication, update your website software, check your SSL certificate, remove unused plugins, and confirm your backups can be restored. Then build a regular maintenance routine so your website stays protected as your business grows. Just as high-security locks safeguard your physical business premises, strong cybersecurity measures help protect your digital assets from unauthorized access.
A secure website protects more than data. It protects your reputation, your search visibility, your customer relationships, and the trust that keeps people coming back to your Birmingham business.